What We Never Touch: Cutting Admin While Protecting Client Data
For CPA firms and insurance agencies: how we cut repetitive admin and speed up client follow-ups while keeping tax returns and policy files off-limits.
Picture this: in a busy CPA firm in the middle of February, partners are still chasing clients for missing tax forms and prior-year schedules. Every evening, someone opens a spreadsheet, checks the portal, and types another round of reminder emails. Or for example, in an independent insurance agency, commercial account managers spend their mornings copying policy numbers and coverage limits onto routine certificates of insurance and chasing renewal questionnaires.
Owners in both professions know how much skilled payroll and billable capacity disappears when professionals spend hours every week on repetitive follow-ups and clerical handoffs. Yet the moment an outside consultant suggests automating part of the office, the managing partner or agency principal asks the same question: what happens to our client data?
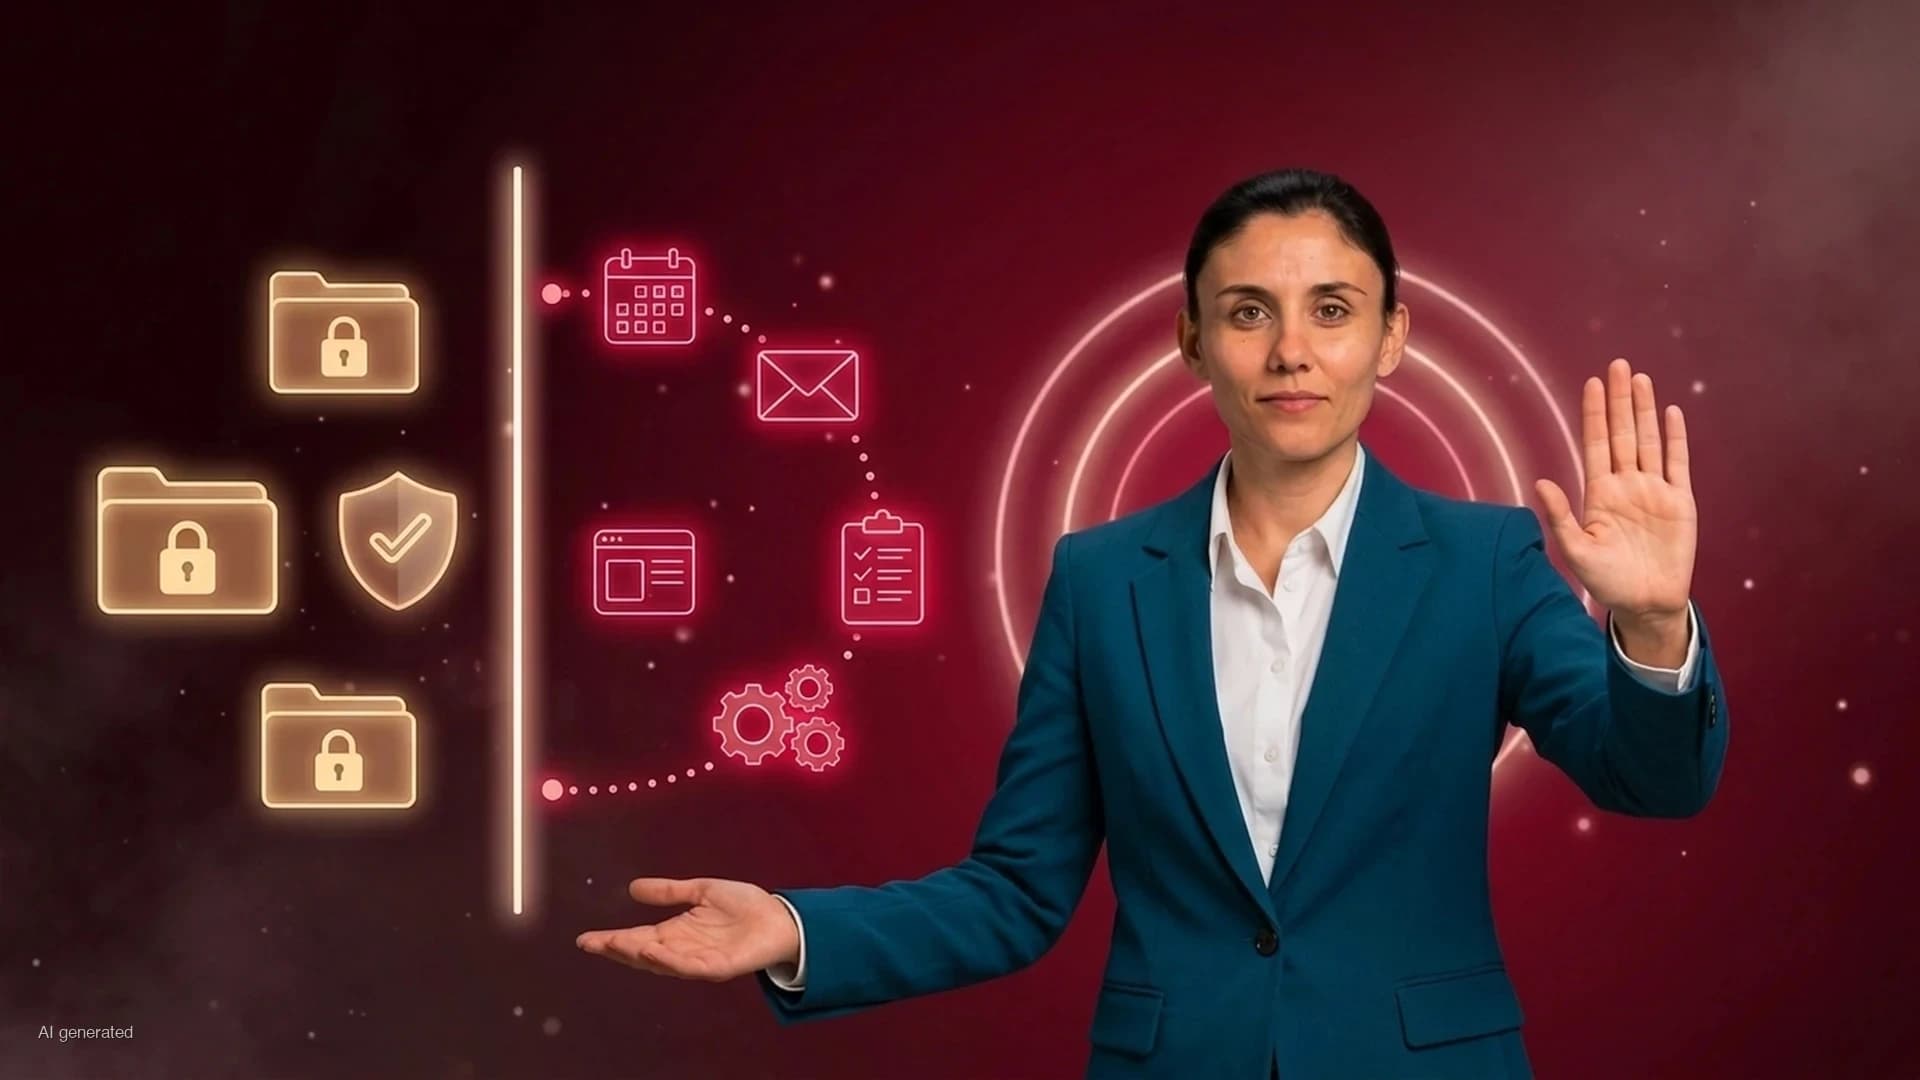
Our starting point is simple: you decide what a workflow touches, and the first fix can stay out of your sensitive client records altogether. Here is how we prefer to set a plain-English data boundary with accounting firms and independent insurance agencies before we build anything.
Key points
- We separate office plumbing (status tracking, follow-up reminders, handoffs that speed up client replies) from sensitive client records (tax returns, Social Security numbers, underwriting files).
- We prefer to start with a first fix that operates on workflow steps and blank templates rather than live taxpayer files or private policy documents.
- We write down the data boundary for the firm owner to approve before any change is built, so it fits your existing security plan.
Why CPAs and insurance principals guard the door
If you run a tax practice or an independent agency, your caution is not stubbornness. It is your job, and it is backed by federal and state law.
At the same time, the pressure on your staff is real. According to the June 2026 AICPA PCPS CPA Firm Top Issues Survey, reported by CPA Practice Advisor on June 23, 2026 and the Journal of Accountancy in June 2026, hiring experienced staff ranked as the number one issue for firms with 11 to 30 professionals, while firms across size brackets also pointed to technology change management and data security concerns.
Independent insurance agencies report the same tension between capacity and security. In the Big "I" 2026 Agency Universe Study, reported by Insurance Journal on September 24, 2026, 45% of agencies named finding and screening job candidates with strong potential as their top overall challenge. While 46% of independent agencies reported using AI in 2026, up from 15% in 2024, the two biggest barriers were lack of knowledge about capability at 60% and security and privacy concerns at 48%.
Experienced practitioners who have succeeded with automation address that tension by keeping client files out of the experiment. In the Journal of Accountancy's August 1, 2026 feature on small accounting firms, Florida practitioner Cheryl Hannafin, CPA, explained her rule in one sentence: "I generally use AI to build the plumbing rather than to handle client data." In that same August 1, 2026 article, Brian Davis, CPA, noted that no client data is provided to a public platform and that a human reviews the process and makes final decisions.
What federal rules require you to protect
For CPA and tax firms, protecting client records is a statutory obligation. As the Internal Revenue Service states in IRS Publication 4557 (Rev. June 2024), Safeguarding Taxpayer Data: A Guide for Your Business, protecting taxpayer data is the law, and under the Gramm-Leach-Bliley Act, professional tax return preparers are defined as financial institutions subject to the Federal Trade Commission (FTC) Safeguards Rule.
In IRS Publication 4557 (Rev. June 2024), the IRS and FTC lay out concrete requirements that every firm owner must enforce:
- Maintain a written information security plan appropriate to your firm's size, complexity, and the sensitivity of the customer information you handle.
- Limit access to customer and taxpayer information strictly to individuals who have a legitimate business reason to see it.
- Implement multi-factor authentication requiring at least two authentication factors for anyone accessing customer information on your system.
- Select service providers that maintain appropriate safeguards, require those safeguards by contract, and oversee how customer information is handled.
Independent insurance agencies operate under state insurance data security laws and carrier agreements governing personally identifiable information, driver's license numbers, claims histories, and financial records. When an outside vendor asks to connect an unvetted tool directly to your tax software, document portal, or agency management system on day one, they are asking you to take on unnecessary compliance risk. We prefer to start outside those sensitive systems.
Plumbing versus payload: how we draw the line
To make the boundary clear for you and your staff, we divide office work into two categories: the plumbing and the payload.
The payload is your clients' private information. When we scope a first fix, we prefer to keep it out of:
- Tax returns, W-2s, 1099s, K-1s, or client financial statements.
- Social Security numbers, Employer Identification Numbers, or Identity Protection PINs.
- Bank account numbers, routing numbers, or credit card details.
- Insurance underwriting files, loss runs, driver's license numbers, or medical disclosures.
- Unredacted client folders inside your tax software, secure portal, or agency management system.
The plumbing is how your team tracks whether a task has started, where it is waiting, and who needs a reminder. That includes blank intake forms, status columns on an internal checklist, email reminder templates that contain no sensitive numbers, and internal notifications telling an account manager or tax senior what is ready for review. We usually start by fixing the plumbing so your team keeps custody of the payload.
How we cut admin work and delays without client files
During our Operations Audit, Mariela maps how work moves through your office and builds the first fix so you can see it working before deciding on anything else. Because we are based in Europe, we work remotely and meet on video, which is why we prefer a clear, written boundary with US firms from the start.
For example, suppose a CPA firm ties up senior staff pay every week because partners and seniors chase clients by email for missing tax documents. To map and fix that kind of bottleneck, the first fix can stay out of your tax software and the documents your clients upload. We usually start by looking at a blank organizer checklist and how your team marks an item as "requested" or "received." A workflow inside your existing Microsoft 365 or practice management environment can send scheduled reminders until your staff checks the "received" box, while the actual tax forms go straight into your encrypted client portal.
For example, suppose an independent insurance agency wants to clear routine follow-ups and intake prep off the commercial account managers' desks. Instead of giving an outside tool access to carrier portals or policy files, we prefer to start with how incoming requests are logged and tracked, or how renewal questionnaires are followed up when a client has not replied. When a draft email or checklist is prepared, it waits for a licensed team member to review and send.
As we explain in how to map the process before you automate it, we can start by examining the process with blank templates and a plain description of the steps, and write down which information a workflow may read, which actions require human approval, and which areas remain outside the project. When a rule is ready to be configured inside your own software account, your administrator enters the credentials and keeps the keys.
Putting the boundary in writing before anything is built
Before we build the first fix in our audit, we write down the data boundary in plain English as part of our governance checklist:
- Which internal tools or status fields the workflow is allowed to read.
- Which systems and folders remain off-limits.
- Where a human on your team reviews and approves the output before a client sees it.
- How your office manager or IT administrator can pause or turn off the workflow.
You can see how our process works on our services page, or read what happens in our 15-minute Free Efficiency Assessment to see how our first conversation runs.
If you want to free your team from repetitive admin without putting client data at risk, Book Your Free Efficiency Assessment with Mariela.